Virtual CIO & technology advisory · Taunton & UK-wide


Technology decisions your board can actually sign off.

I provide the technology leadership a full-time CIO would, for a set number of days each month: strategy, budget, risk, board reporting, and holding your suppliers to account. Every sector, from owner-managed businesses to London Stock Exchange listed groups. Fee-only: I take no commission from any vendor, reseller or IT provider.

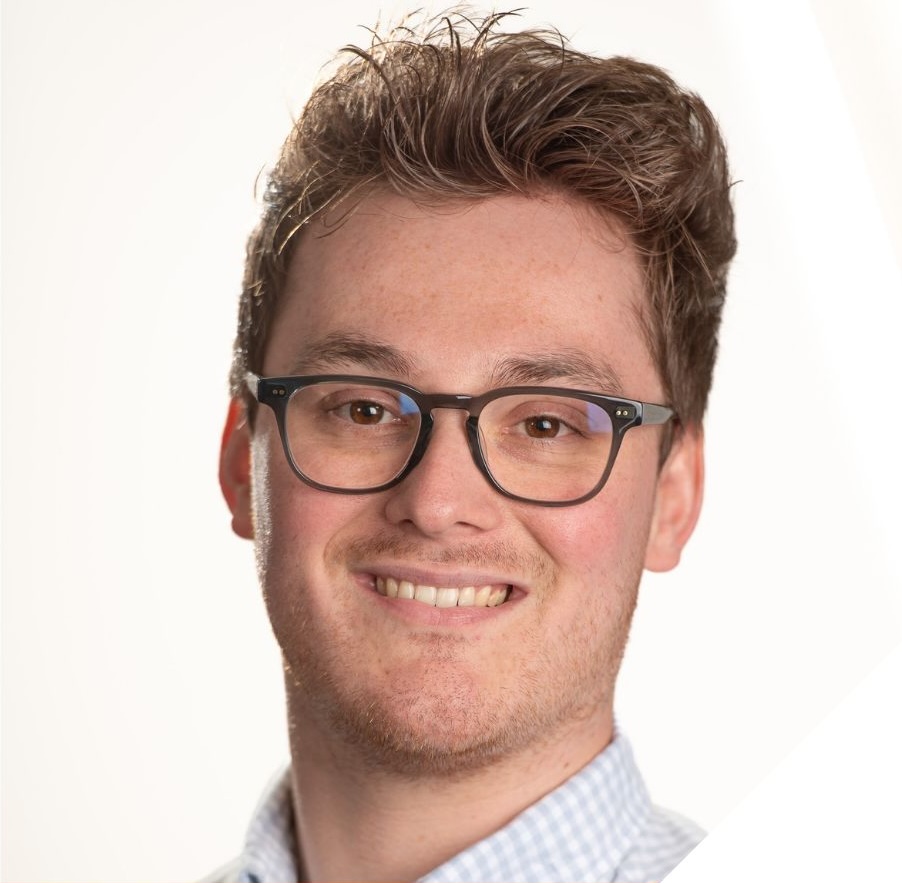
Oliver Thomas, Principal Consultant and Virtual CIO at Thomas & Co. Systems
Oliver Thomas
Principal Consultant & vCIO
Board exposure
LSE-listed board and subsidiary leadership
Budget accountability
£500,000 annual IT budget
Certifications architected
ISO 27001 & 9001, from nothing to certified
Enterprise remediation
FTSE 100 financial services group
Commercial position
No vendor income of any kind
The remit

Most organisations do not have an IT problem. They have a decision problem — nobody in the room can say what the technology should cost, which risks are being carried, or what happens to any of it in eighteen months.

That gap is what I fill, as a business partner rather than a supplier. Most organisations have nobody at board level who can speak to technology with authority, and no realistic case for a full-time CIO salary to fix it. I take that seat for the days each month it needs filling: strategy, budget, security governance and supplier accountability, reported to the board rather than buried inside an IT function.

The output is not a report that sits in a drawer. It is a costed roadmap, a risk register your auditors accept, and a supplier arrangement that has been read by someone with no stake in it.

I have done this job from the inside. Nine years in enterprise IT — developer, infrastructure engineer, IT manager, then head of IT services with a nine-person team and a £500,000 budget — before a year as virtual CIO to a portfolio of twelve corporate clients, among them a London Stock Exchange listed group. I know what I am asking your suppliers to do, because I have done it.

Services

Four areas of work, one accountable person

Engagements usually combine all four. On advisory work I direct and assure delivery rather than perform it: your team or your provider executes, and I am accountable for whether it was the right thing to do and whether it was done properly. I have run the delivery end myself for most of my career, which is precisely why I know what to hold people to.

01 · Leadership

Board representation & IT strategy

  • The technology voice at your board or leadership meetings
  • Multi-year technology roadmap, costed and sequenced
  • IT budget construction, profit and loss, and capital versus operating spend forecasting
  • Quarterly board and audit-committee reporting
  • M&A technology due diligence and post-deal integration oversight
What you receive

A board-ready technology strategy paper, a three-year investment model, a supplier scorecard and a standing quarterly report written for non-technical directors — the kind of reporting I have presented to a London Stock Exchange listed board and its subsidiary leadership.

02 · Governance

Security governance & certification

  • ISO 27001 and ISO 9001 programmes led from gap analysis to certification
  • Cyber Essentials and Cyber Essentials Plus readiness, with remediation directed
  • Risk register construction and board risk appetite
  • UK GDPR and Data Protection Act alignment
  • Security posture assessment, with findings tracked to closure
  • Business continuity and recovery requirements set, and tested against
What you receive

A complete Information Security Management System — policy set, risk register, control mapping, internal audit schedule and management review pack — built to pass external certification audit. I own the framework and chair the programme; your team and providers carry out the technical remediation. I have taken an organisation from no framework at all to full ISO 27001 and 9001 certification as lead architect, so I know what an auditor will and will not accept.

03 · Architecture

Architecture direction & technical assurance

  • Target architecture defined and documented, for your provider to build to
  • Supplier designs, migration plans and change proposals reviewed and challenged
  • Identity and access standards: Entra ID, single sign-on, multi-factor authentication and privileged access
  • Microsoft 365 and Azure security posture reviewed against recognised benchmarks
  • Device, endpoint and remote-working standards set and audited
  • Data protection, retention and information-handling policy
What you receive

A documented target architecture and a set of standards your provider builds to, plus an independent read on where you stand today, measured against Microsoft Secure Score and equivalent benchmarks. On an advisory engagement I define what good looks like, challenge what is proposed and confirm what was actually delivered, rather than performing the build myself. Having run a standardised endpoint programme across more than 500 devices, I know when a plan will not survive contact with reality.

04 · Oversight

Supplier, spend & service oversight

  • Independent review of your IT provider against a defined scorecard
  • Contract, licensing and renewal review, with negotiation support
  • Supplier selection and tendering run on your behalf
  • Service level agreements defined, measured and enforced
  • Licence rationalisation and removal of unused subscriptions
  • Management information and reporting your board can act on
What you receive

A supplier scorecard, a licensing position you can defend, and reporting that answers board questions rather than raising them. Most advisers reviewing your service desk have never run one. I have — a nine-engineer multi-tier desk, a full helpdesk platform migration reaching a 98.7% service-level success rate, and Power BI reporting putting production against sales forecasts in front of directors. That is the standard I hold your provider to.

Sectors

Every sector, every size

Technology governance is sector-agnostic. The questions a board must answer about cost, risk and resilience do not change between an insurance group and a manufacturer. What changes is the regulation you sit under and the way the business runs day to day — and establishing both is the first week of any engagement.

Financial services & insuranceFTSE 100 group security remediation
Investment & acquisitionsBoard advisory and M&A integration
Manufacturing & industrialsFour-site operations, £35M turnover
Professional servicesISO certification and Cyber Essentials Plus
LegalClient confidentiality and Lexcel alignment
Healthcare & carePatient data protection and records governance
Construction & engineeringMulti-site and mobile workforce
Logistics & distributionOperational reporting and continuity
Retail & hospitalityPayment environments and seasonal scaling
EducationSafeguarding, identity and device estates
Charity & not-for-profitConstrained budgets, funder assurance
Public sector supply chainTender-driven certification requirements
Engagements delivered Ready to deliver

Owner-managed & SME

Usually the first time anyone has produced a costed plan. The work is establishing a baseline, removing licensing waste and getting a defensible security position in place, often alongside an existing IT provider.

Mid-market & multi-site

Where technology stops being a support function and starts constraining growth. Operational reporting, standardised device estates, and a board with numbers it can plan against.

Large, listed & regulated

Audit committees, external assurance, insurer scrutiny and M&A activity. The reporting line is formal, the evidence requirements are real, and the risk register has to withstand challenge.

Independence

I am paid by my clients, and by nobody else.

It sounds like a technicality. It changes every recommendation I make. Most technology advice in the UK comes from someone who also sells the technology, and that advice is priced accordingly — usually into the licence.

  • No commission, margin, rebate or referral fee From any vendor, reseller, distributor or managed service provider. No exceptions, and no small print.
  • Your contracts read by someone with no stake in them Licence counts, renewal terms, uplift clauses and out-of-scope definitions, reviewed against what you are receiving.
  • I understand how this industry prices Four years working inside managed service providers, latterly as virtual CIO. I know how these services are packaged and which service level agreements are meaningful.
  • Fixed scope, fixed fee, clean exit Diagnostics and roadmaps are quoted as a fixed fee. Retainers run on sixty days' notice, either side, with no minimum term beyond that.
Engagement

How an engagement runs

Nobody signs a retainer with someone they have met once. Every engagement starts with a fixed-scope, fixed-fee diagnostic, and you are free to stop there.

01

Diagnostic

Two to three weeks. I review your architecture, contracts, licensing, security posture and governance, interview your people and your incumbent provider, and establish what you are spending, and what you are getting for it.

Deliverable
Findings paper with prioritised, costed recommendations
Commitment
Fixed fee, no follow-on obligation
02

Strategy & roadmap

Four to six weeks. The findings become a sequenced three-year plan with budget envelopes, dependencies, risk decisions framed for the board, and an explicit statement of which risks you are choosing to accept.

Deliverable
Board-approved roadmap, investment model and risk register
Commitment
Fixed fee against defined scope
03

Retained or interim

Ongoing, if you want it. I take the technology seat at your board or leadership meetings, chair delivery against the roadmap, hold suppliers to the plan and act as the technology voice in the room between meetings. Also available as interim cover while you recruit or through a leadership gap. Governance programmes such as ISO 27001 or Cyber Essentials Plus can be led as standalone, fixed-scope engagements.

Deliverable
Quarterly board pack, supplier oversight, roadmap ownership
Commitment
Monthly retainer in days, or a defined interim term. 60 days' notice either side
Assessment

Governance maturity check

Eight questions across the four domains a board is usually asked about after something has gone wrong. The output is a register rated red, amber or green — the same format I use in client reporting — so you can see how I work as well as where you stand.

Technology governance register

Indicative only. This is a structured self-assessment, not an audit, and it cannot see your configuration. Nothing you enter is transmitted or stored.

Answer honestly rather than aspirationally — the amber results are the useful ones.

Indicative governance register

Distinction

Where this sits alongside your IT provider

Both roles are necessary, and I am not trying to replace your provider. They are different jobs, and one of them cannot objectively review the other.

Dimension Thomas & Co. Systems Managed service provider
Question answered What should we do, what will it cost, and what are we risking? Is it working, and how quickly can we fix it?
Commercial alignment Fee-only. No commission, margin, rebate or referral income. Revenue typically includes licence resale, hardware margin and vendor rebates.
Reports to The board or owner directly. An IT manager, operations lead or office manager.
Governance depth Full information security management system, certifiable risk register, audit-committee reporting. Endpoint protection, patching and monitoring against a service-level agreement.
Supplier oversight Reviews and challenges your incumbent provider on your behalf. Cannot audit itself.
Hands-on delivery Directed and assured, not performed. Oversight stays separate from delivery. Performs the work, and is paid for performing it.
Commercial model Fixed-fee diagnostics; retainers scoped in days per month. Per-seat monthly fee plus project and out-of-scope billing.

In practice I work with incumbent providers far more often than against them. A good provider generally welcomes a client who knows what they want.

Track record

Selected engagements

Work delivered between 2018 and 2026, some as a client engagement and some as an in-house programme — each is labelled. I no longer take on hands-on delivery: this is the experience behind the judgement, and the reason I can tell whether a supplier's plan is sound before you pay for it. I do not name clients, and I do not discuss the detail of their environments. Confidentiality outlasts an engagement, and an adviser who discusses one client's business will discuss yours.

FTSE 100 · Financial services & insurance

Privileged access programme

Led a security programme for a FTSE 100 group, reporting directly to their Director of Technology. Designed and delivered a privileged access model in Microsoft 365 using Privileged Identity Management, alongside tenant-wide data loss prevention.

Outcome
A privileged access standard adopted at group level, with elevation time-bound and logged. Client specifics remain confidential.
LSE-listed group · Board advisory

Board advisory & M&A integration

Lead technology strategist to a London Stock Exchange listed group, advising the board and subsidiary leadership on infrastructure and post-acquisition systems integration.

Outcome
Portfolio grown to twelve corporate accounts, ten of them onboarded within the first six months.
In-house programme · IT services firm

ISO 27001 & 9001 from a standing start

As lead architect, independently designed and implemented both management systems for my employer, an IT services business, where no formal framework previously existed: policy set, risk register, control mapping, internal audit schedule and management review.

Outcome
Full certification achieved against both standards. I know what an external auditor will and will not accept, because I have sat on the other side of it.
£35M turnover · Manufacturing

Multi-site operations & reporting

Designed and deployed cross-site barcoding and logistics tracking across four manufacturing facilities, with Power BI dashboards putting sales against production in front of directors in real time.

Outcome
Inventory accuracy improved across all four sites; zero operational downtime through the COVID-19 disruption, with full remote-working capability delivered in weeks.
In-house programme · Service transformation

Service desk rebuild & platform migration

Migrated service delivery from Freshservice to Halo PSA while directing a multi-tier, nine-engineer service desk and holding full accountability for a £500,000 annual IT budget. Founded an internal IT Academy on Microsoft Learn.

Outcome
98.7% service-level success rate following migration, with a measured uplift in customer satisfaction.
In-house programme · 500+ devices

Managed endpoint build at scale

Engineered a standardised, automated endpoint management solution across more than 500 devices using Microsoft Intune, Windows Autopilot and Apple Business Manager, replacing inconsistent manual provisioning.

Outcome
Repeatable zero-touch device provisioning across mixed Windows and Apple estates, replacing manual builds.
Fees

How fees work

No hourly billing, no open-ended scopes and no surprises on the invoice. Fee ranges are shared in the first call, before any scoping work begins.

Phase 01

Diagnostic

Fixed fee · 2–3 weeks

  • Architecture, contract and licensing review
  • Security posture and governance assessment
  • Stakeholder and incumbent provider interviews
  • Prioritised, costed findings paper
  • No obligation to continue
Phase 02

Strategy & roadmap

Fixed fee · 4–6 weeks

  • Three-year sequenced roadmap
  • Investment model and budget envelopes
  • Board-ready risk register
  • Supplier strategy and scorecard
  • Presented to your board in person
Phase 03

Retained vCIO

Monthly · scoped in days

  • Defined days per month, not open availability
  • Quarterly board and audit-committee reporting
  • Supplier oversight and contract renewals
  • Roadmap ownership and delivery chairing
  • 60 days' notice, either side

Standalone governance programmes — ISO 27001 or ISO 9001 certification, Cyber Essentials Plus readiness, a supplier tender, or an independent review of your current provider — are quoted separately against scope, headcount and site count. All fees exclude VAT. Travel within the South West is included; travel beyond it is charged at cost and agreed in advance.

Questions

The questions people actually ask

How is a virtual CIO different from our existing IT provider?

Your provider keeps systems running. A virtual CIO decides what those systems should be, what they should cost, and which risks the board is knowingly carrying. The roles are complementary. I work alongside incumbent providers regularly, and part of the value is holding them to a standard on your behalf — which a client rarely has the time or leverage to do alone.

Do you carry out the implementation work yourself?

On a retained advisory engagement, no — and that is deliberate. I set the strategy, define the standards and hold whoever delivers to them: your internal team, your existing provider, or a specialist I help you select. Keeping delivery separate from oversight is the point, because the person checking the work should not be the person being paid to do it. It also keeps my fees predictable and my attention on your board rather than on a project plan. I have spent most of my career on the delivery end, so this is a choice about how advisory engagements are best structured, not a limit on what I can do.

Do you resell hardware, software or licences?

No. I take no commission, margin, rebate or referral fee from any vendor, reseller or managed service provider. I am paid by my clients and by nobody else. If I recommend a supplier, that recommendation is the whole of my interest in the outcome.

You have worked inside managed service providers. Why should we trust your view of ours?

Because I know how the model works from the inside. I spent a year as virtual CIO within an MSP and three years running service delivery at another, so I understand how these services are packaged and priced, and which service level agreements are meaningful. I also carried a monthly sales target in that role. I do not carry one now, and that is the difference worth paying for.

Which sectors do you work in?

All of them. Technology governance is sector-agnostic: the questions a board must answer about cost, risk and resilience do not change between an insurance group and a manufacturer. What changes is the regulatory overlay and the operational constraint, and establishing those is the first week of any engagement. Engagements delivered to date span financial services and insurance, investment and acquisitions, manufacturing and industrials, and professional services.

What size of organisation do you work with?

From owner-managed businesses through to London Stock Exchange listed groups. I have run IT for a £35M turnover manufacturer across four sites, held a £500,000 budget with a nine-engineer team, advised the board of a listed group, and led security remediation inside a FTSE 100 financial services group. The discipline is the same at every size; the reporting line and the pace change.

How long have you been doing this independently?

Thomas & Co. Systems launched in 2026, so you are entitled to ask. Before that: nine years in enterprise IT — developer, infrastructure engineer, IT manager, then head of IT services running a nine-person team and a £500,000 budget — followed by a year as virtual CIO to a portfolio of twelve corporate clients including an LSE-listed group.

We already have an internal IT manager. Does this still make sense?

Often it makes more sense. A capable IT manager who has never presented to a board needs a translation layer, not a replacement. I set the strategy and carry the board reporting; your manager keeps operational ownership and usually develops quickly with the structure in place. I have been that IT manager, which helps.

How much of your time does a retainer include?

Retainers are specified in days per month against a defined scope, not open-ended availability. Every retainer states what is included, what is chargeable separately, and the notice period on both sides — sixty days, either way.

Do you work outside the South West of England?

Yes. I am based in Taunton, Somerset and work across the United Kingdom, on site where the engagement needs it and remotely where it does not. Board meetings, workshops and audits are worth travelling for; a licensing review is not.

What happens after the roadmap is delivered?

That is your decision, and there is no obligation to continue. Some clients take the roadmap and execute it with their existing provider. Others retain me to chair delivery, hold suppliers to account and report to the board through the programme. Both are legitimate outcomes.

Principal

Oliver Thomas

Principal Consultant & Virtual CIO

I started as a systems developer inside a manufacturer, worked up through infrastructure and service management, and ended up presenting technology risk to the board of a listed investment group. The consistent lesson across all of it is that the technology is rarely the hard part. The hard part is getting a board to make an informed decision, and then holding everyone — including the suppliers — to it.

I hold a First Class BSc in Business & Information Systems from the University of Hertfordshire, where I was awarded the University Prize for the highest recorded result on the programme. Since then I have architected ISO 27001 and ISO 9001 certification from a standing start, led security remediation inside a FTSE 100 financial services group, carried a £500,000 IT budget with a nine-engineer team, and advised a portfolio of twelve corporate clients as virtual CIO. I work with organisations of every size and in every sector, and I will tell you early if I am not the right fit.

2026 – present Principal Consultant & vCIOThomas & Co. Systems · Taunton, working UK-wide
2025 – 2026 Virtual Chief Information OfficerNexus Open Systems, Exeter · twelve-client portfolio, LSE-listed group advisory
2022 – 2025 Head of IT Services & Customer ExcellenceSRD Technology UK, Taunton · ISO 27001 & 9001, £500k budget, nine engineers
2021 – 2022 IT ManagerOffsite Solutions, Highbridge · £35M turnover, four manufacturing sites
2018 – 2021 IT Infrastructure & Support EngineerOffsite Solutions, Highbridge
2017 – 2018 Junior Systems DeveloperOffsite Solutions, Highbridge
2015 – 2016 Industrial placementDell, Bracknell

Qualifications

  • BSc (Hons) Business & Information Systems — First Class, 79%, University of Hertfordshire
  • University Prize — highest recorded result on the programme
  • CMI Level 5 Certificate in Management & Leadership
  • Microsoft 365 Certified: Fundamentals (MS-900)
  • Microsoft Certified: Azure Fundamentals (AZ-900)
  • Veeam Technical Sales Professional (VMTSP)
  • Cisco Networking Academy; PRINCE2 and Agile foundations at degree level

Platforms I know from the inside

  • Microsoft 365, Azure, Entra ID, Intune, Windows Autopilot
  • Apple Business Manager, Miradore MDM
  • VMware vSphere, Veeam backup and replication
  • Halo PSA, Autotask, KaseyaOne suite, Freshservice
  • Power BI, SQL for reporting and data work
  • ISO 27001 and ISO 9001 control frameworks, ISMS portals
Full career history on LinkedIn →
Contact

Arrange an introductory call

Thirty minutes, no charge, no obligation. If there is no sensible engagement here I will say so on the call rather than send you a proposal.

Areas of interest (select all that apply)

I reply to every enquiry personally, usually within one working day. Your details are used only to respond to you and are never shared — see the privacy notice.

Legal

Privacy notice

What personal data is collected, why, how long it is kept, and your rights under UK data protection law. Last updated 25 July 2026, version 1.0.